 by
Introduction
The cryptocurrency industry has experienced another major cybersecurity crisis following a massive cyber attack on Binance, one of the world’s largest cryptocurrency exchanges. The security incident, which came to light on October 29, 2026, reportedly resulted in approximately $6.3 billion worth of cryptocurrency assets being affected by unauthorized withdrawals from Binance’s hot wallet infrastructure.
The incident has raised serious questions about cryptocurrency exchange security, digital asset protection, blockchain technology, and the ability of even the world’s largest trading platforms to defend themselves against sophisticated cybercriminals.
Binance confirmed that it was investigating a serious security incident and subsequently disclosed that the estimated financial impact was approximately $6.3 billion. The company also stated that it would cover the losses using its Secure Asset Fund for Users (SAFU) and corporate resources. According to Binance’s October 30 security update, approximately $3 billion in affected assets had been frozen through cooperation with blockchain intelligence companies, cryptocurrency issuers, and other industry partners.
The attack has become a major discussion point among cryptocurrency investors, cybersecurity professionals, blockchain developers, financial institutions, and regulatory authorities.
This article examines the Binance cyber attack, its possible causes, the reported methods used by attackers, its financial consequences, Binance’s response, and the future of cryptocurrency security.
1. What Happened in the Binance Cyber Attack?
On October 29, 2026, Binance experienced a serious security incident involving unauthorized cryptocurrency withdrawals from its hot wallet infrastructure.
The incident initially attracted attention after unusual transactions involving large amounts of digital assets were detected on blockchain networks. Cryptocurrency analysts and blockchain monitoring companies began examining suspicious wallet movements and reporting potentially unauthorized transfers.
Binance acknowledged the security issue and began an investigation. As a precaution, the exchange temporarily suspended withdrawals while its security teams examined affected infrastructure and implemented additional controls.
In its October 30 announcement, Binance estimated the total impact at approximately $6.3 billion.
This incident is particularly significant because of the reported scale of the affected assets. It demonstrates that cryptocurrency exchanges face serious security challenges even when they have extensive technical infrastructure and dedicated cybersecurity teams.
Binance also explained that its investigation initially suggested a compromised laptop belonging to a DevOps engineer might have provided attackers with access to internal systems. Subsequent investigations uncovered additional potential breach points.
The company stated that it had found no evidence that wallet private keys had been leaked.
However, the complete technical explanation remained under investigation as of October 31, 2026.
2. How Did Hackers Attack Binance?
One of the most important questions surrounding the Binance security incident is how attackers managed to initiate unauthorized cryptocurrency withdrawals.
According to Binance’s preliminary investigation, a compromised laptop belonging to a DevOps engineer may have played a role in the incident.
DevOps engineers work with systems that support software development, deployment, infrastructure management, and operational processes. These systems can sometimes have access to sensitive internal services.
If an attacker compromises an employee’s device, the attacker may attempt to exploit the access available to that employee or use the device as an entry point into other internal systems.
Binance reported that the suspected compromise allowed an unauthorized party to access service containers and submit unauthorized withdrawal transactions.
Later investigation updates indicated that the incident involved additional breach points and was more complex than initially understood.
Blockchain investigators also examined the possibility that transaction-signing infrastructure had been compromised.
Transaction-signing systems are particularly important because cryptocurrency transactions must be authorized before funds can move from controlled wallets.
A successful compromise of the systems responsible for approving transactions can create serious financial consequences, even if attackers do not obtain direct access to every private key.
The full attack sequence has not been independently established in the information available as of October 31, 2026.
3. The Role of Binance Hot Wallets
To understand the attack, it is important to understand how cryptocurrency exchanges manage digital assets.
Most large cryptocurrency exchanges use a combination of hot wallets and cold wallets.
What Is a Hot Wallet?
A hot wallet is a cryptocurrency wallet connected to the internet or an online system. It allows exchanges to process transactions, facilitate withdrawals, and provide liquidity for customers.
Hot wallets are important because exchanges handle thousands or millions of transactions. Keeping all operational funds offline would make normal trading and withdrawal services difficult.
However, internet-connected wallets introduce additional cybersecurity risks.
Potential threats include:
- Unauthorized access to wallet infrastructure.
- Compromised employee devices.
- Stolen authentication credentials.
- Malware infections.
- Social engineering attacks.
- Exploitation of vulnerable software.
- Unauthorized transaction approvals.
- Compromised internal services.
What Is a Cold Wallet?
Cold wallets store cryptocurrency offline or in systems isolated from ordinary internet-connected infrastructure.
They are generally considered safer against many online attacks because remote attackers cannot directly access an offline wallet through a normal internet connection.
However, cold storage is not a complete security solution. Organizations must also protect backup systems, access procedures, signing devices, recovery mechanisms, and employees responsible for managing digital assets.
The Binance incident highlights why cryptocurrency platforms need multiple layers of security rather than relying on a single protection mechanism.
4. How Much Money Was Affected?
The estimated financial impact of the Binance cyber attack was approximately $6.3 billion, according to the exchange’s October 30 security announcement.
This figure makes the incident one of the most significant cryptocurrency security events ever reported.
The attack affected the cryptocurrency industry beyond Binance because it raised concerns about the security of centralized exchanges and the risks associated with storing digital assets on third-party platforms.
Binance stated that approximately $3 billion in affected assets had been frozen through cooperation with industry partners.
The recovery effort involved blockchain intelligence firms, law enforcement agencies, cryptocurrency issuers, and other organizations.
Binance also announced that it would cover the financial impact using its SAFU fund and corporate treasury.
The company reported setting aside more than $6.34 billion in company funds to cover the affected assets.
These commitments are important because exchange security incidents can damage customer confidence, even when a platform promises to reimburse affected users.
For investors, the central concern is not simply how much cryptocurrency was transferred. It is whether the exchange can demonstrate that customer balances remain protected and that its infrastructure is sufficiently secure.
5. Who Was Behind the Binance Cyber Attack?
The identity of the attackers remains an important part of the investigation.
Blockchain intelligence company TRM Labs reportedly identified similarities between the Binance incident and previous attacks associated with North Korean-linked hacking groups.
Some investigators have connected the incident to a group known as TraderTraitor, which has previously been associated with major cryptocurrency thefts.
However, attribution in cybersecurity investigations is complicated.
Hackers may use stolen infrastructure, cryptocurrency mixing services, multiple blockchain networks, and sophisticated transaction patterns to make investigations more difficult.
Investigators generally examine several types of evidence, including:
- Cryptocurrency transaction histories.
- Wallet addresses and fund movements.
- Previously identified attacker infrastructure.
- Malware and technical indicators.
- Similarities with earlier cyber incidents.
- Blockchain intelligence reports.
- Information from law enforcement investigations.
It is important to distinguish between an investigative assessment and an officially established identity.
As of October 31, 2026, Binance had not publicly confirmed the identity of the individuals responsible for the attack.
The investigation remains ongoing.
6. Binance’s Immediate Response to the Security Breach
Following the discovery of the security incident, Binance introduced several emergency security measures.
The company’s immediate priority was to contain the incident, protect users, prevent additional unauthorized transactions, and investigate the affected systems.
Its reported response included the following actions:
Temporary Suspension of Withdrawals
Binance temporarily suspended withdrawals while its security teams conducted additional checks.
This measure was designed to prevent further unauthorized activity while the exchange examined the integrity of its infrastructure.
Although temporary withdrawal restrictions can create inconvenience for customers, they can be necessary during a serious security investigation.
Revocation of Affected Authorizations
Binance reported that it had revoked affected authorizations and introduced additional controls.
Revoking compromised permissions is an important security measure because it can prevent unauthorized systems or accounts from continuing to access sensitive infrastructure.
Blockchain Investigation
Binance worked with blockchain intelligence companies and cryptocurrency industry partners to trace affected assets.
Blockchain transactions are publicly recorded, which allows investigators to examine transaction histories and identify suspicious wallet activity.
However, tracing cryptocurrency does not automatically guarantee recovery.
Cooperation With Law Enforcement
The exchange also reported cooperation with law enforcement agencies and other industry organizations.
Cross-border cooperation is particularly important because cryptocurrency transactions can move between multiple blockchain networks and jurisdictions.
Financial Protection for Users
Binance stated that it would cover the losses associated with the incident using SAFU and corporate resources.
This commitment is intended to protect customers from bearing the financial consequences of the security breach.
7. What Is the SAFU Fund?
The Secure Asset Fund for Users, commonly known as SAFU, is Binance’s emergency protection fund.
It was established to provide an additional financial safety mechanism for users in exceptional circumstances, including certain security incidents.
The fund is an important part of Binance’s risk-management strategy.
Cryptocurrency exchanges face different types of risks, including:
- Cyber attacks.
- Unauthorized withdrawals.
- Operational failures.
- Security vulnerabilities.
- Infrastructure disruptions.
- Unexpected financial losses.
An emergency reserve can help an exchange respond to a major incident without immediately transferring the entire financial burden to customers.
In its October 30, 2026 announcement, Binance said it would use SAFU and corporate funds to cover the losses associated with the incident.
However, investors should understand that an emergency fund does not prevent cyber attacks. It is a financial protection mechanism rather than a replacement for strong cybersecurity controls.
8. Impact of the Binance Hack on Cryptocurrency Markets
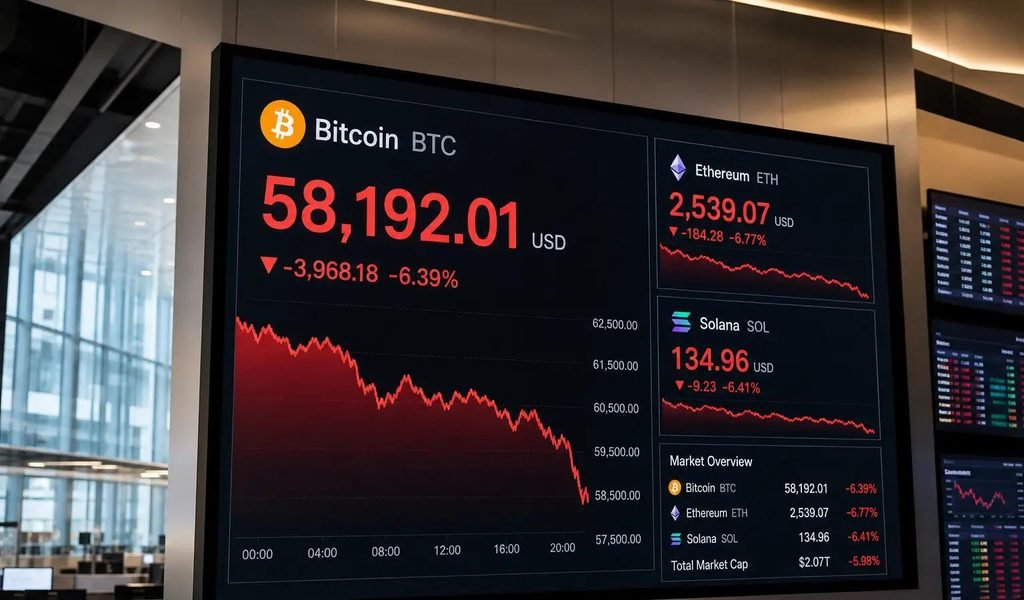
The Binance security incident created uncertainty throughout the cryptocurrency market.
Large-scale cryptocurrency thefts can affect market sentiment because investors may begin questioning the safety of digital assets held on centralized trading platforms.
Bitcoin, Ethereum, BNB, and other cryptocurrencies may experience price volatility when investors respond to major exchange-related news.
The reported Binance attack also highlighted several market risks.
Investor Confidence
Cryptocurrency investors depend on exchanges to provide secure access to their assets.
When a major platform experiences a significant security incident, customers may become more cautious about leaving large cryptocurrency balances on centralized exchanges.
Cryptocurrency Price Volatility
News about exchange security incidents can increase buying and selling pressure.
Some investors may sell assets because they fear further market disruptions, while others may see price declines as investment opportunities.
Stablecoin Concerns
Stablecoins are widely used in cryptocurrency trading and cross-border digital payments.
During the Binance investigation, stablecoin issuers reportedly froze certain assets linked to the incident.
This demonstrates an important feature of some centralized stablecoins: their issuers may have the technical ability to restrict or freeze particular tokens.
Institutional Investment
Large financial institutions evaluate custody, operational security, counterparty risk, and regulatory compliance before investing in digital assets.
A major exchange security incident can encourage institutional investors to demand stronger security standards and more transparent risk-management procedures.
9. Why Are Cryptocurrency Exchanges Targets for Hackers?
Cryptocurrency exchanges are attractive targets because they manage large amounts of valuable digital assets and operate complex technical infrastructure.
Unlike traditional financial institutions, cryptocurrency transactions can be difficult to reverse once they have been confirmed on a blockchain.
This creates significant opportunities for criminals who successfully compromise wallet infrastructure or transaction authorization systems.
There are several reasons why exchanges face cybersecurity threats.
Large Digital Asset Holdings
Exchanges manage substantial cryptocurrency reserves and process enormous transaction volumes.
A successful attack can potentially generate significant financial rewards for criminals.
Complex Technology Infrastructure
Modern exchanges use cloud computing, distributed systems, APIs, wallet infrastructure, databases, authentication systems, and blockchain integrations.
Each component requires appropriate security controls.
Human Security Weaknesses
Employees are often targeted through phishing emails, social engineering, compromised devices, and stolen credentials.
Even strong technical security systems can be weakened when attackers obtain legitimate access through compromised employees or devices.
Global Operations
Cryptocurrency exchanges operate internationally and must manage different legal requirements, technical environments, and security challenges.
Their global operations can increase the complexity of incident response.
Irreversible Transactions
Many blockchain transactions cannot simply be reversed by contacting a payment provider.
Once funds move through multiple wallets and networks, recovering them can become difficult.
10. Major Cybersecurity Risks Facing Binance
The Binance security incident demonstrates that cryptocurrency exchanges must continuously improve their cybersecurity infrastructure.
Modern cybercriminals do not necessarily target blockchain technology itself. They may instead target the computers, employees, software, cloud services, and internal systems that support cryptocurrency transactions.
Some of the most important cybersecurity risks include:
Phishing Attacks
Phishing involves fraudulent emails, websites, or messages designed to trick individuals into revealing passwords, authentication codes, or other sensitive information.
Cryptocurrency employees and customers can both become targets.
Insider Threats
An insider threat occurs when someone with legitimate access to an organization’s systems intentionally or unintentionally creates a security risk.
Exchanges must carefully manage employee permissions and monitor sensitive activities.
Malware and Ransomware
Malicious software can compromise computers, steal information, or disrupt business operations.
Organizations need endpoint protection, security monitoring, and regular software updates.
Cloud Infrastructure Vulnerabilities
Cryptocurrency platforms frequently depend on cloud services.
Incorrect configurations, weak access policies, and insufficient monitoring can expose sensitive internal systems.
API Security Problems
Application programming interfaces allow different software systems to communicate.
Poorly protected APIs can create opportunities for unauthorized access and data exposure.
Social Engineering
Social engineering involves manipulating people into performing actions that compromise security.
Security awareness training and strict verification procedures are essential defenses.
11. What Should Binance Users Do After the Cyber Attack?
The Binance incident has understandably created concerns among cryptocurrency investors.
Users should avoid making emotional decisions based on unverified social media reports.
Instead, they should follow practical security measures.
- Check official announcements: Follow Binance’s official website and verified communication channels for updates.
- Secure account credentials: Use a unique and strong password.
- Enable two-factor authentication: Add an additional authentication layer wherever available.
- Review account activity: Examine recent logins, withdrawal records, and security notifications.
- Check withdrawal settings: Review withdrawal addresses and available security restrictions.
- Avoid suspicious links: Never click unknown links claiming to provide emergency Binance support.
- Never share authentication codes: Legitimate support representatives should not need your password or one-time verification codes.
- Beware of recovery scams: Criminals may impersonate blockchain investigators and promise to recover stolen cryptocurrency in exchange for advance payments.
Users should also understand that an exchange’s promise to cover losses does not eliminate every possible account-level risk.
Anyone who suspects unauthorized activity should contact Binance through its official support channels.
12. The Importance of Two-Factor Authentication
Two-factor authentication (2FA) is an important component of cryptocurrency account security.
It requires users to provide an additional verification factor beyond their password.
For example, an account may require a password and a separate authentication code.
Common authentication methods include:
- Authenticator applications.
- Hardware security keys.
- Passkeys.
- Biometric authentication.
- Other supported verification methods.
However, users should understand that two-factor authentication does not protect against every type of cyber attack.
An exchange’s internal infrastructure can have security weaknesses that are separate from an individual customer’s login credentials.
Therefore, cryptocurrency security requires protection at multiple levels.
13. How Blockchain Technology Helps Investigate Cryptocurrency Theft
Although blockchain networks can be targeted by criminals, their public transaction records can also help investigators.
Most public blockchains maintain transparent transaction histories.
This means investigators can examine wallet activity, identify suspicious transfers, and follow cryptocurrency movements between addresses.
Blockchain analytics companies use specialized tools to identify relationships between wallet addresses and investigate potentially illicit transactions.
These tools can help investigators:
- Trace cryptocurrency transfers.
- Identify suspicious wallet activity.
- Monitor transactions across supported networks.
- Detect connections with previously identified addresses.
- Support law enforcement investigations.
- Coordinate with cryptocurrency exchanges and token issuers.
However, blockchain transparency does not mean every stolen asset can be recovered.
Attackers may transfer assets between different networks, exchange cryptocurrencies, or use services that make tracing more difficult.
The Binance incident illustrates the importance of cooperation between exchanges, blockchain intelligence firms, cryptocurrency issuers, and law enforcement agencies.
14. The Role of Cryptocurrency Issuers in Freezing Stolen Assets
One notable aspect of the Binance security incident was the reported cooperation of cryptocurrency issuers.
Certain stablecoin issuers can restrict or freeze tokens associated with suspicious activity under their applicable policies and technical controls.
This ability can help prevent criminals from freely transferring or using certain stolen assets.
According to reports published on October 30, 2026, Tether and Circle were among the organizations that froze assets associated with the incident.
Other industry partners also participated in efforts to trace and restrict affected funds.
This raises an important question about the balance between decentralization and centralized control.
Bitcoin transactions, for example, cannot ordinarily be frozen by a single issuing company because Bitcoin has no central token issuer.
Some centrally issued stablecoins, on the other hand, include administrative controls that may allow issuers to restrict particular addresses.
The incident demonstrates how cooperation across the cryptocurrency industry can support asset recovery.
15. How Can Binance Prevent Similar Cyber Attacks in the Future?
Preventing another incident of this scale requires a comprehensive security strategy.
No single cybersecurity product or technology can guarantee complete protection.
Binance and other cryptocurrency exchanges can strengthen their defenses through several important measures.
Stronger Employee Device Security
Employee laptops and workstations should receive regular security updates and continuous monitoring.
Organizations should also restrict access to sensitive systems from devices that do not meet established security requirements.
Zero-Trust Security Architecture
Zero-trust security operates on the principle that no user or device should automatically receive access simply because it is connected to an organization’s internal network.
Every access request should be evaluated according to identity, permissions, device security, and context.
Multi-Party Transaction Authorization
High-value cryptocurrency transactions should require multiple independent approvals.
This reduces dependence on a single account, employee, or authorization mechanism.
Continuous Security Monitoring
Security teams should continuously monitor unusual account activity, infrastructure changes, authentication events, and transaction patterns.
Automated alerts can help identify suspicious behavior earlier.
Regular Security Audits
Independent cybersecurity experts should examine exchange infrastructure, wallet management systems, cloud environments, and internal access controls.
Security audits can identify weaknesses before criminals exploit them.
Improved Incident Response
Exchanges should maintain tested incident response plans.
These plans should clearly define responsibilities, emergency procedures, communication channels, and recovery priorities.
Stronger Wallet Segmentation
Exchanges should limit the amount of cryptocurrency exposed to internet-connected infrastructure and separate sensitive wallet operations from ordinary business systems.
These improvements can reduce risk and make successful attacks more difficult.
16. Binance Cyber Attack Compared With Previous Cryptocurrency Hacks
The Binance incident is part of a broader history of cryptocurrency exchange security failures.
Over the years, several major cryptocurrency platforms have experienced attacks involving stolen funds, compromised systems, or unauthorized transactions.
One of the most significant recent examples was the February 2025 Bybit attack, in which approximately $1.5 billion in cryptocurrency was stolen.
The Bybit incident demonstrated the financial capabilities of sophisticated attackers and the risks associated with digital asset custody.
Other historical incidents have also affected cryptocurrency exchanges and blockchain projects.
These events reveal recurring industry problems, including:
- Weak access controls.
- Compromised employee devices.
- Inadequate transaction verification.
- Wallet management vulnerabilities.
- Third-party service risks.
- Insufficient security monitoring.
The October 2026 Binance incident further reinforces the need for continuous investment in cryptocurrency cybersecurity.
17. The Future of Cryptocurrency Exchange Security
The cryptocurrency industry is evolving rapidly.
As digital assets become more widely used, exchanges will need to meet increasingly demanding security expectations.
Investors want reliable trading platforms, secure withdrawals, transparent asset reserves, and effective customer protection.
Regulators are also paying greater attention to cybersecurity, operational resilience, and the protection of customer assets.
Future improvements may include:
- Advanced artificial intelligence-based threat detection.
- Stronger identity verification.
- Hardware-backed authentication.
- Improved wallet isolation.
- More sophisticated transaction monitoring.
- Independent security assessments.
- Real-time suspicious activity detection.
- Stronger international cooperation.
Artificial intelligence may help security teams identify unusual activity more quickly. However, cybercriminals can also use AI to improve phishing campaigns, automate certain malicious activities, and create more convincing fraudulent communications.
Consequently, cryptocurrency exchanges must continuously adapt their security strategies.
18. What Does the Binance Hack Mean for Cryptocurrency Investors?
The Binance cyber attack provides several important lessons for cryptocurrency investors.
First, the reputation of an exchange should never be considered a guarantee of complete security.
Even major platforms can experience serious cybersecurity incidents.
Second, investors should understand the difference between exchange custody and self-custody.
When users leave cryptocurrency on an exchange, they depend on that exchange to maintain secure custody and provide access to their assets.
Self-custody gives individuals more direct control over their cryptocurrency, but it also makes them responsible for protecting their private keys and recovery phrases.
Third, diversification and risk management remain important.
Investors should carefully consider how much cryptocurrency they keep on any single platform.
Finally, users should evaluate security announcements using reliable information rather than social media rumors.
The Binance incident demonstrates why security awareness is an essential part of cryptocurrency investing.
19. Is Binance Still Safe to Use After the Cyber Attack?
Whether Binance is safe to use after the October 2026 security incident depends on the outcome of its investigation, the effectiveness of its remediation measures, and its ability to demonstrate that affected infrastructure has been secured.
Binance announced that it would cover the losses associated with the incident and provide updated information about its reserves.
The company also said it was working to restore withdrawal services after completing additional security checks.
Nevertheless, investors should not treat any exchange as completely risk-free.
Before using a cryptocurrency platform, customers should consider:
- The exchange’s security history.
- Its transparency regarding customer assets.
- Its withdrawal and account protection policies.
- Its incident response procedures.
- Its regulatory status in the relevant jurisdiction.
- The quality of its customer support.
- Its independent security assessments.
Users should follow official announcements before making decisions about deposits or withdrawals during a security incident.
20. Conclusion: Lessons From the Binance Cyber Attack 2026
The Binance cyber attack of October 29, 2026, represents a major cybersecurity challenge for the global cryptocurrency industry.
With an estimated impact of approximately $6.3 billion, the incident has highlighted the risks associated with cryptocurrency exchange infrastructure, hot wallet security, employee device protection, and transaction authorization systems.
Binance responded by suspending affected withdrawal services, investigating the incident, cooperating with blockchain intelligence firms and law enforcement, and committing to cover the financial losses.
The reported freezing of approximately $3 billion in affected assets also demonstrates the importance of cooperation between cryptocurrency exchanges and digital asset issuers.
However, the incident raises broader questions about the future of centralized cryptocurrency platforms.
As cryptocurrency adoption increases, exchanges must invest in stronger cybersecurity infrastructure, independent audits, secure wallet management, employee protection, and transparent incident reporting.
For investors, the most important lesson is that digital asset security should never be taken for granted.
Cryptocurrency offers significant opportunities, but those opportunities come with technical, financial, and operational risks.
The Binance incident is a reminder that trust in the cryptocurrency industry must be supported by strong security systems, responsible management, and continuous improvement.
The future success of cryptocurrency exchanges will depend not only on trading volume and technological innovation but also on their ability to protect the digital assets entrusted to them.